tools/rebuild_pages.sh rebuilds the site within 5 minutes of a change; by hand: python3 -B tools/site.py.1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---
How we proved it never halts
#3's proof in a mirror, from a different start
#3 counts a binary number down on a list of pairs of blocks, like an odometer running backward, and its proof is a checklist of inequalities showing that a block only ever runs out where that is harmless. This machine is #3's table seen in a mirror, with left and right swapped and the state letters renamed, started in the state that is #3's D. Watching it is like watching #3 in a mirror: the same countdown, with the head working at the right end of the tape.
What is new is the opening. After 78,911 steps the run reaches the mirror image of the checkpoint #3's argument starts from (#3 gets there after 78,710 steps), except that the last pair has 25 copies of 01 instead of 24, which the checklist allows. From there #3's argument (the nine moves and the checklist, none of which depends on the start) applies unchanged, so it never halts. As far as the two runs have been simulated side by side, they then make the same move every time, with the one extra copy moving around among the blocks at the far end; the proof does not need this.
The Rocq file contains #3's whole proof for #3's own table and adds the 78,911-step opening from state D. It then checks that this table, mirrored and renamed, is exactly #3's, and uses two busycoq theorems (mirroring a machine or renaming its states does not change whether it halts) to carry the result over.
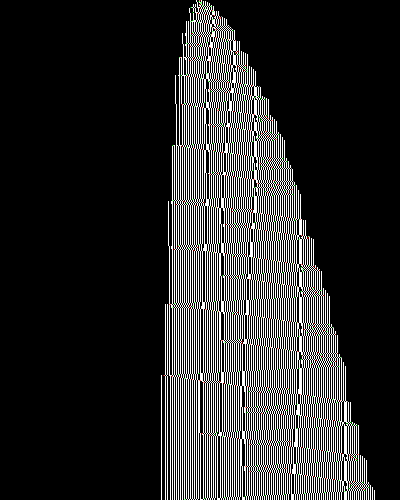
About this picture
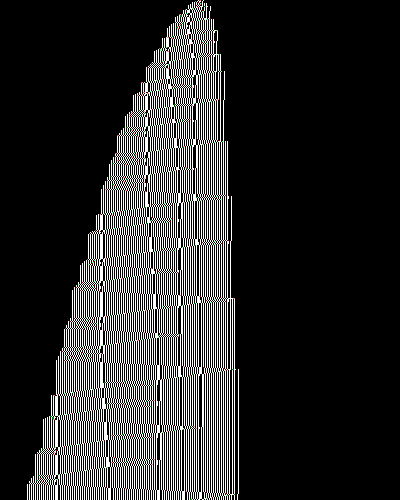
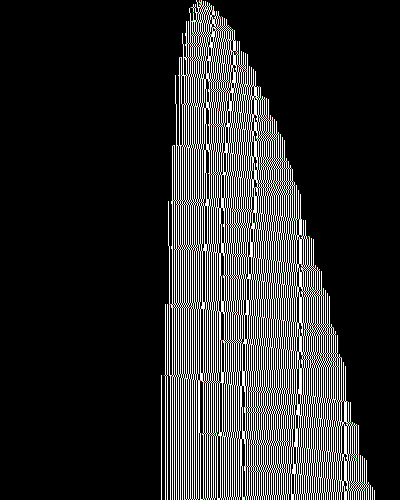
The standard picture (bbchallenge.org's Default view): each row is the whole tape at one step, time runs downward, and the head's path draws the pattern.
Overview
In one sentence
#3's table, mirrored, with a different start. Flip every direction (L↔R) and rename the states by φ: A→D, B→A, C→B, D→C, E→E, F→F, and you get #3's table, all 12 entries. φ is the only one of the 720 × 2 maps that does this. The twin starts in A, and φ(A) = D, so it is #3's machine run from 0^inf D> 0^inf: a different orbit of the same macro map. (submission/README.md, Mechanism)
- Upstream
- Kill claimed · PR #15merged 2026-10-13 12:25 UTC by ccz181078 ·
Sk1Class2_v1.v · TM4· on Submissions → - Rocq proof
- check_kill PASS · first Oct 10 10:211,364 lines · 65 KB .v · compile 39.9 s · coqchk pass · 0 axioms · PASS Oct 10 10:21 (re-run Oct 10 17:29) · from #3· the .v file
- Automatic review
- 6 of 6 checks passtemplate: #3's kill file (kill 4) (twin: parent kill's .v) · details in Proof →
- Class
- Skelet 1-like Class 2
- On the list
- not on
BB6_holdouts_663.txt(line 586 of the previous list) · historical 740 line 586 - Derived from
1RB0LD_#3 Kill claimed1RC0RA_ 1RD1RF_ 1LA0LE_ 1RE1LD_ 0RB---
Mechanism
What to check here: the pictures show the mechanism that the rule table describes.
Figures
One row per counter decrement, every 4th cell drawn. Watch the vertical and slanted colour edges, and where they kink.
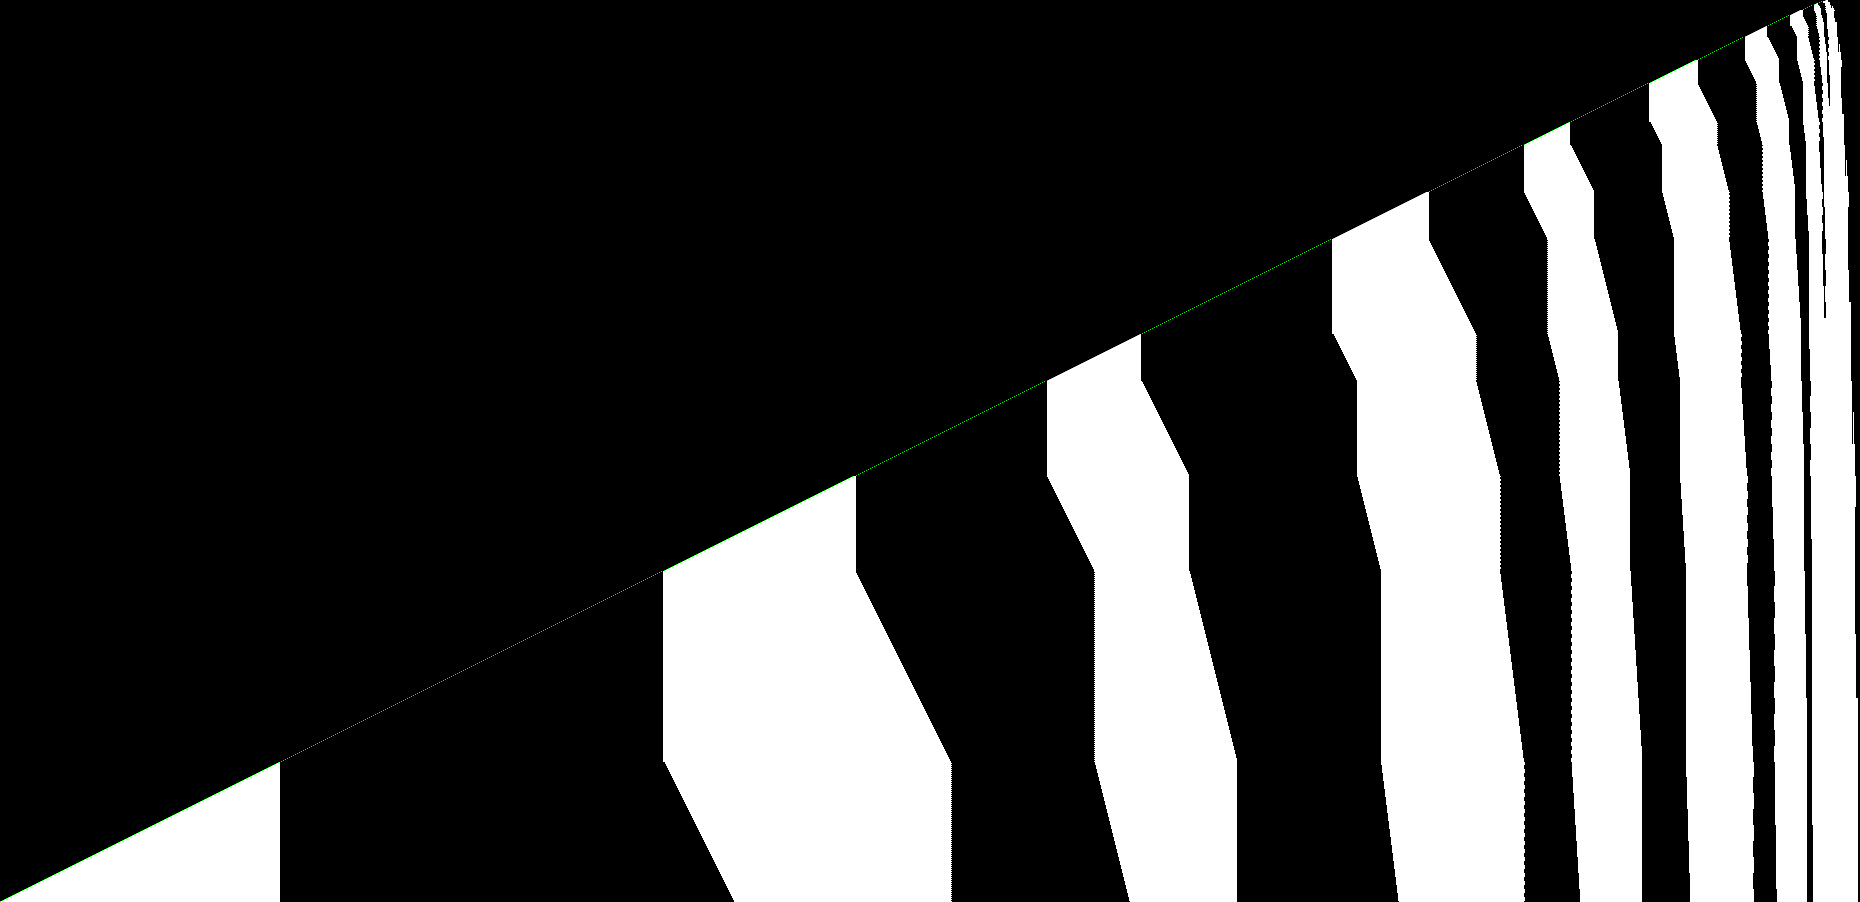
Every step from counter value 12. Compare how far each long sweep reaches over three decrements.
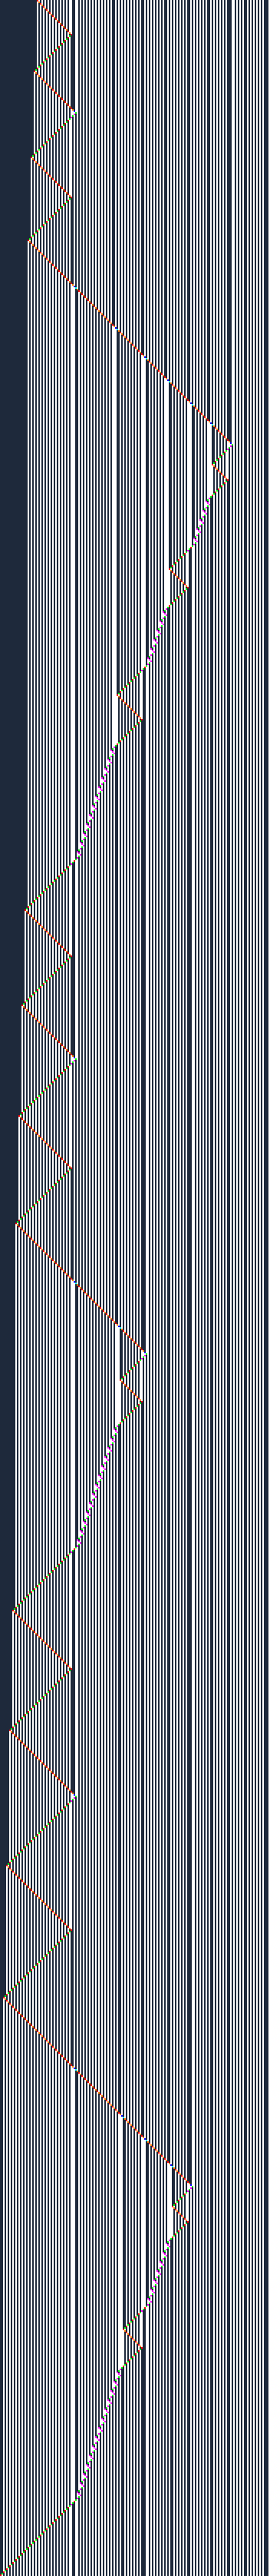
The top-right corner of Fig 1, every cell drawn. Follow purple blocks and blue/orange borders down the rows.
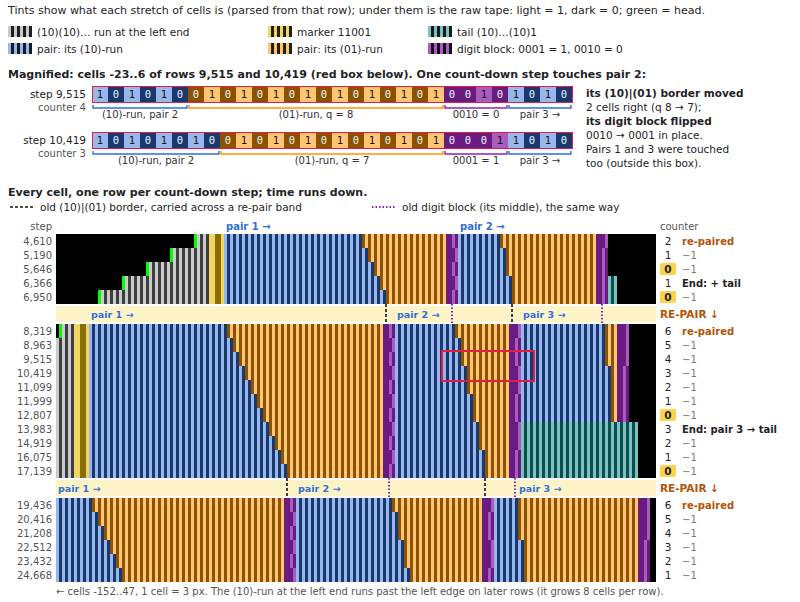
More figures (3)Fig 4–6: Blaze (speed mode), 100M steps · Snapshot every 1M steps, to 1 billion · bbchallenge default view, first 10,000 steps
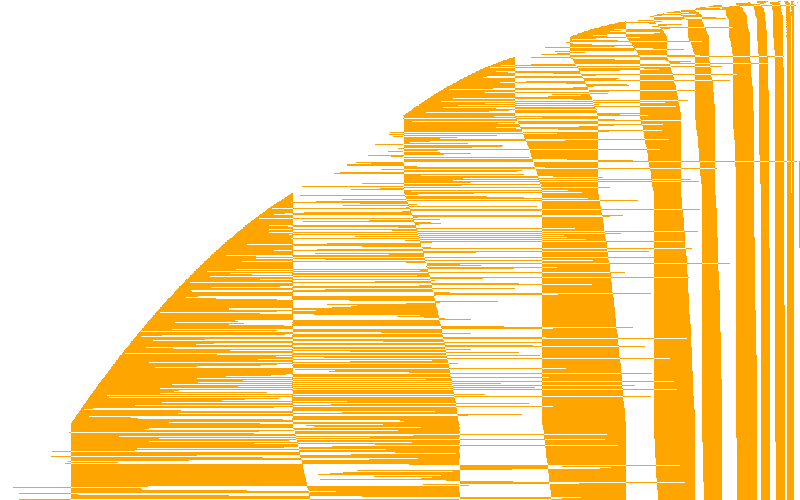
Sampling every 16th cell turns the pair list into orange/white bands; band edges are pair boundaries.
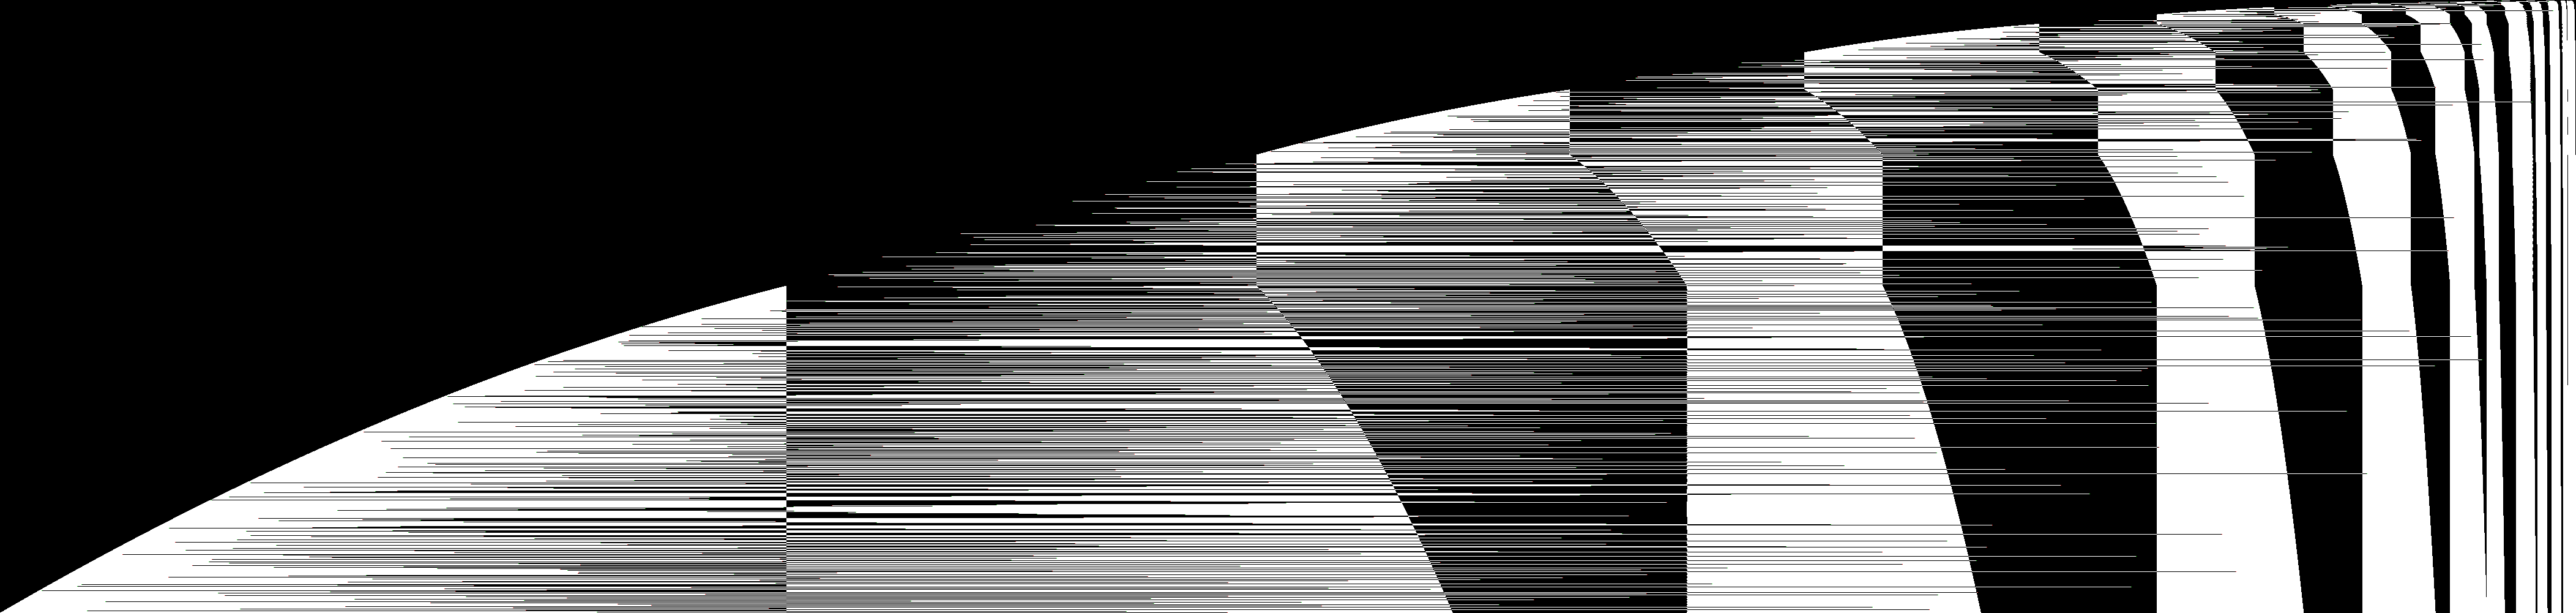
The same band picture out to 1e9 steps; the left edge grows like sqrt(t).
The site's view: the tape grows mainly to the left; the right end barely moves.
Rules (6/6 validated)exact tape rewrites the proof will formalize, each re-checked by simulation
| rule | from ⟶ to | cases | steps | checked |
|---|---|---|---|---|
| Dec | 0∞ <A (10)h 11001 Π_{i<k}[(10)a_i (01)b_i+1 0010] (10)p (01)q+1 0001 R ⟶ 0∞ <A (10)h+4 11001 Π_{i<k}[(10)a_i+1 (01)b_i 0001] (10)p+1 (01)q 0010 R | k=0..L-1 (borrow chain); b_i>=1, q>=1; any h mod 4; R = remaining pairs + any tail | — | ✓48/48 |
| DecMerge | 0∞ <A (10)h 11001 Π_{i<k}[(10)a_i (01)b_i+1 0010] (10)p (01) 0001 (10)p2 (01)q2 s R ⟶ 0∞ <A (10)h+4 11001 Π_{i<k}[(10)a_i+1 (01)b_i 0001] (10)p+p2+3 (01)q2 s R | q hits 0 on a 1->0 digit: fuse with next pair; last pair fuses into tail: (10)^p (01) 0001 (10)^t 1 -> (10)^(p+t+3) 1 | — | ✓36/36 |
| End | 0∞ <A (10)h 11001 Π_{i<L}[(10)a_i (01)b_i+1 0010] (10)p (01)q+1 0010 0∞ ⟶ 0∞ <A (10)h+4 11001 Π_{i<L}[(10)a_i+1 (01)b_i 0001] (10)p+1 (01)q 0010 101 0∞ | all digits 0, no tail; b_i>=1, q>=1. q=0 (EndLast): last pair becomes tail (10)^(p+4) 1, validated 36/36 | — | ✓36/36 |
| Ov | 0∞ <A (10)h 11001 (10)a_1+1 (01)b_1 0010 Π_{j=2..L}[(10)a_j (01)b_j 0010] (10)t 1 0∞ ⟶ 0∞ <A (10)2 11001 (10)h+5 (01)a_1 0010 Π_{j<L}[(10)b_j (01)a_(j+1) 0001] (10)b_L (01)t+1 0001 0∞ | all digits 0, tail present; a_1>=1; new counter value 2^(L+1)-2 | — | ✓36/36 |
| X1 | 0∞ <A (10)h 11001 (10)a_1+1 (01)b_1 0010 Π_{j=2..L-2}[(10)a_j (01)b_j 0010] (10)a (01) 0010 (10)b (01) 0010 0∞ ⟶ 0∞ <A (10)2 11001 (10)h+5 (01)a_1 0010 Π_{j<L-2}[(10)b_j (01)a_(j+1) 0001] (10)b_(L-2) (01)a 0010 (101)2 (01)b+3 0∞ | End with the last two q = 1 (seen once, step 251,973,021) | — | ✓30/30 |
| X2 | 0∞ <A (10)h 11001 Π_{j<L}[(10)a_j (01)b_j+1 0010] (10)p (01)q+1 0010 (101)2 (01)k 0∞ ⟶ 0∞ <A (10)h+4 11001 Π_{j<L}[(10)a_j+1 (01)b_j 0001] (10)p+1 (01)q 0010 (10)3 (01)k 0001 0∞ | all digits 0 with tail (101)^2(01)^k; returns to the normal family | — | ✓30/30 |
Compressed historythe tape as 0∞ <A (10)h 11001 (10)p1 (01)q1 s(d1) (10)p2 (01)q2 s(d2) ... (10)pL (01)qL s(dL) T 0∞ [s(1)=0001, s(0)=0010; T = '' | (10)t 1 | (101)2 (01)k] at 24 moments: where the rules are read off
| step | h | L | V=sum d_j 2^(j-1) | p1 | q1 | p2 | q2 | pL | qL | T |
|---|---|---|---|---|---|---|---|---|---|---|
| 1,845 | 2 | 2 | 2 | 11 | 11 | 10 | 2 | 10 | 2 | - |
| 4,610 | 2 | 2 | 2 | 23 | 14 | 7 | 16 | 7 | 16 | - |
| 8,319 | 2 | 3 | 6 | 23 | 26 | 10 | 9 | 14 | 2 | - |
| 19,436 | 2 | 3 | 6 | 47 | 32 | 16 | 15 | 4 | 20 | - |
| 34,137 | 2 | 4 | 14 | 47 | 56 | 22 | 21 | 18 | 2 | - |
| 78,710 | 2 | 4 | 14 | 95 | 68 | 34 | 33 | 1 | 24 | - |
| 137,547 | 2 | 5 | 30 | 95 | 116 | 46 | 45 | 22 | 2 | - |
| 276,384 | 2 | 4 | 14 | 159 | 132 | 78 | 65 | 6 | 43 | - |
| 368,693 | 2 | 5 | 30 | 95 | 180 | 110 | 89 | 41 | 2 | - |
| 598,490 | 2 | 5 | 30 | 191 | 140 | 134 | 133 | 3 | 47 | - |
| 868,551 | 2 | 6 | 62 | 191 | 236 | 94 | 157 | 45 | 2 | - |
| 1,637,772 | 2 | 5 | 30 | 383 | 284 | 142 | 141 | 14 | 84 | - |
| 2,053,945 | 2 | 6 | 62 | 191 | 428 | 238 | 165 | 82 | 2 | - |
| 3,050,262 | 2 | 6 | 62 | 383 | 284 | 334 | 285 | 11 | 88 | - |
| 4,178,299 | 2 | 7 | 126 | 383 | 476 | 190 | 381 | 86 | 2 | - |
| 7,335,144 | 2 | 7 | 126 | 767 | 572 | 286 | 285 | 8 | 92 | - |
| 11,309,893 | 2 | 8 | 254 | 767 | 956 | 382 | 381 | 90 | 2 | - |
| 23,109,954 | 2 | 8 | 254 | 1,535 | 1,148 | 574 | 573 | 5 | 96 | - |
| 38,479,639 | 2 | 9 | 510 | 1,535 | 1,916 | 766 | 765 | 94 | 2 | - |
| 84,867,492 | 2 | 9 | 510 | 3,071 | 2,300 | 1,150 | 1,149 | 2 | 100 | - |
| 145,833,457 | 2 | 10 | 1,022 | 3,071 | 3,836 | 1,534 | 1,533 | 98 | 2 | - |
| 252,225,526 | 2 | 9 | 254 | 4,095 | 4,092 | 2,814 | 2,045 | 28 | 63 | (101)^2 (01)^102 [X1] |
| 277,337,206 | 1,022 | 10 | 767 | 4,350 | 3,837 | 2,942 | 1,917 | 3 | 102 | - [X2] |
| 466,254,879 | 2 | 11 | 2,046 | 6,143 | 5,628 | 2,558 | 3,581 | 100 | 2 | - |
hlast 2Llast 11V=sum d_j 2^(j-1)last 2,046p1last 6,143q1last 5,628p2last 2,558q2last 3,581pLlast 100qLlast 2Tlast -Template comparisonSBCv6.v TM21: partly applies · the nearest solved proof, what carries over, and the transitions that differ
| 0 | 1 | |
|---|---|---|
| A | 1RB | 0LD |
| B | 1RC | 0RA |
| C | 1RD | 1RF |
| D | 1LA | 0LE |
| E | 1RE | 1LD |
| F | 0RB | --- |
- file
SBCv6.v:3702- module
TM21- machine
1RB1LB_0LC1RD_0RA1LC_0RB1RE_0RD0LF_---1LE(11 transitions apart)- diff
8 of 11 defined transitions differ under the best state renaming (no mirror); Sk1like_TC_v1/v2 machines differ in 8-9- note
- Same architecture (pair list + counter sweeps + overflow re-pairing + finite tail states = TM21's LIncs/Ov/LH1-3), but not its shapes: from TM21's init config this machine halts in 4,539 steps. Sk1like_TC (eventual cycler via native_compute) doesn't fit.
Proof & checks
Kill 8 · Skelet 1-like Class 2 · the kill file 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---.v: 1364 lines, 142 items · the package submission/
1What is provedCheck: the string, the theorem and every check_kill line are green, and the .v on disk is the one that was checked (same sha256).
1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---sha256 d3ce657f1502916a…
| ✓ | 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---.v | d3ce657f1502916a… = checked |
| ✓ | submission/1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---.v | d3ce657f1502916a… = checked |
All 17 check_kill checks with their one-line results
| ✓ | args | 6x2 machine, framework module Individual62, mode nonhalt |
| ✓ | input | 67041 bytes, 1364 lines, 1500 sentences |
| ✓ | framework | HEAD 0940bb9cf434ba68f0c025dabfde45a219999973 == pin; no tracked changes under verify/ |
| ✓ | framework_build | 13 needed framework .vo files present and fresh, with native code no older than the .vo |
| ✓ | forbidden | none of 30 forbidden patterns occur (ground rule 1's words: anywhere; command words: outside comments and strings; comments never split a token) |
| ✓ | structure | 6 Require name(s) allowed; no top-level Variable/Context; no shadowing; Module/Section balanced |
| ✓ | tm_text | line 34: TM_from_str "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---" == <tm> (41 bytes) |
| ✓ | theorem_text | line 1323: nonhalt : ~halts tm c0 |
| ✓ | coq | coqc 8.20.1 ([local working file] |
| ✓ | names | halts, c0, TM_from_str resolved inside Individual62 |
| ✓ | compile | compiled in 39.9s with all appended checks |
| ✓ | tm_rocq | BB6Kill.Candidate.tm = BusyCoq.Individual62.TM_from_str "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---" by eq_refl (in-file and isolated) |
| ✓ | theorem_rocq | nonhalt : ~ halts (TM_from_str "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---") c0 with absolute names (in-file and isolated) |
| ✓ | isolation | only stock proof plugins loaded; guard/positivity/universe checking on, definitional UIP off |
| ✓ | assumptions | 0 assumption(s), all in the baseline |
| ✓ | coqchk | coqchk -norec BB6Kill.Candidate ok (12.3s); its context summary lists nothing of the file's own |
| ✓ | integrity | input sha256 and framework HEAD/cleanliness identical before and after |
2Same machine as #3?Check: every row of the table is ✓ under the computed renaming (or the listed differences are what status.json's relation says), the two pictures show the same bands, and the trajectory numbers agree with the claimed relation (a twin keeps a fixed small offset; a sibling's gap grows).
status.json names #3 as the parent (1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB---); relation: “twin of #3: #3's table mirrored and renamed, different start state, nearly identical run”. Everything below is computed from the two machine strings, not read from notes.
✓ Identical to #3's table under the renaming A→B, B→C, C→D, D→A, E→E, F→F (#3's state → this machine's), with L and R swapped (mirror image). This machine starts in #3's state D (#3 itself starts in A). The only such map.
| #3 | #3's row (read 0, read 1) | σ | predicted row: renamed by σ, L/R swapped | this machine's actual row | ||
|---|---|---|---|---|---|---|
| A | 1RB 0LD | → B | 1LC 0RA | 1LC 0RA | ✓ | start of #3 |
| B | 1RC 0RA | → C | 1LD 0LB | 1LD 0LB | ✓ | |
| C | 1RD 1RF | → D | 1LA 1LF | 1LA 1LF | ✓ | |
| D | 1LA 0LE | → A | 1RB 0RE | 1RB 0RE | ✓ | start of this machine |
| E | 1RE 1LD | → E | 1LE 1RA | 1LE 1RA | ✓ | |
| F | 0RB --- | → F | 0LC --- | 0LC --- | ✓ |
Rows aligned by σ: each of #3's states X sits next to this machine's state σ(X). ✓ = the actual row equals #3's row with every target state renamed by σ and every move mirrored; --- (halt) must stay ---. Searched: all 720 renamings × with/without mirror.
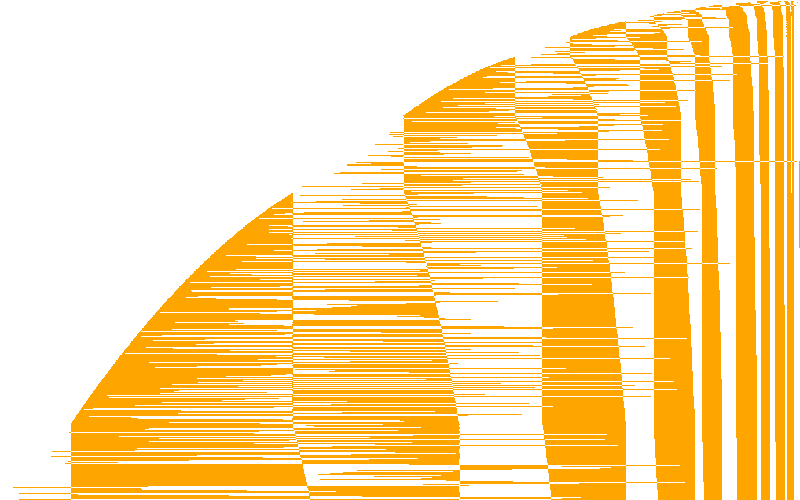
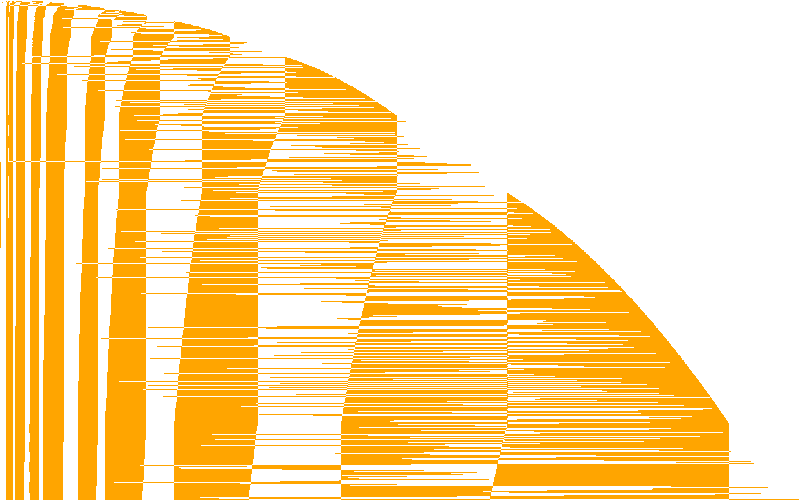
Same view, same settings on both sides. Look for the same band structure: this machine is #3's table mirrored, so expect #3's picture flipped left to right; it starts in #3's state D, not A, so the first steps differ; the numbers below read: trajectory twin, so after the start the bands should match line for line.
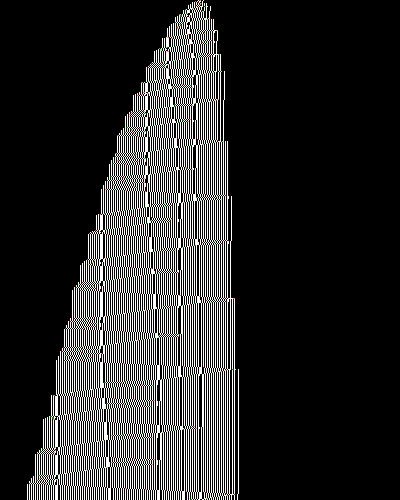
The macro behaviour, identical settings on both sides: each picture is its machine's own visited span stretched to 800 px, so compare the shape and order of the bands, not their absolute width. Speed mode samples one cell per column, so a one-cell shift can swap orange and white inside a band; compare band edges, not colours. Here this machine is #3's table mirrored, so expect #3's picture flipped left to right.
Trajectory numbers, from blank (C core)
✓ trajectory twin: within 0.003% at 1e9 (cells +2, nonzeros +0); the offset stays within 3 at every checkpoint instead of growing
| steps | cells visited (hi − lo + 1) | nonzeros | ||||
|---|---|---|---|---|---|---|
| #3 | this | ratio (Δ) | #3 | this | ratio (Δ) | |
| 1e5 | 672 | 674 | 1.0030 (+2) | 335 | 335 | 1.0000 (+0) |
| 1e6 | 2,260 | 2,262 | 1.0009 (+2) | 1,125 | 1,127 | 1.0018 (+2) |
| 1e7 | 7,443 | 7,445 | 1.0003 (+2) | 3,716 | 3,718 | 1.0005 (+2) |
| 1e8 | 22,096 | 22,098 | 1.0001 (+2) | 11,039 | 11,042 | 1.0003 (+3) |
| 1e9 | 67,343 | 67,345 | 1.0000 (+2) | 33,665 | 33,665 | 1.0000 (+0) |
Each machine from blank in its own start state, sim.py C core. Trajectory twin = cells and nonzeros stay within 16 of the parent's at every checkpoint (a fixed offset from a different start, not a growing gap). Cached in img/vs-parent.json (2026-10-16 10:29 PDT); --force recomputes.
3Where it came fromCheck: the template is the one you expect, and the measured reuse (tiles, the reuse figure, diff) agrees with what the README says was kept and changed (quoted).
The file extends kill #3's .v (1,303 lines; in #3's own package). A script generated it, asserting each edit, and no hand edits were made afterwards. The changes:
tmis the twin, and #3's table becomestm3, with the local-->*/-->+bound to it;solve_initDis busycoq'ssolve_initstarted in D (esxfrom a non-c0start falls back to symbolices, which did not finish);init0, andbasewith far pair (1,25);- #3's
nonhaltbecomesnonhalt_D; - the conjugacy (
phi,perm_twin,nonhalt, about 15 lines).
Every sweep, macro rule, J, Jstep and J_base is #3's text, unchanged, and the file compiled on the first attempt. In all, 22 of #3's lines were replaced and 82 lines added. The file is 1,363 lines and imports only Individual62 from busycoq. It is a direct proof on the holdout string. The second TM_from_str literal (#3's string, as tm3) is the only warning from our checker.
Top two bars: non-blank lines after the TM string is replaced by <TM> and whitespace is collapsed. Bottom bar: our Definitions/Lemmas/… by name.
Other references found:
- loose template vendor/busycoq/verify/SBCv6.v Module TM21 (named in submission/proof.md line 54)
Side-by-side diff: template (1129 lines) vs ours (1172 lines), 65 lines differ; runs of identical lines and long template-only runs folded
| template | ours | ||
|---|---|---|---|
| 18 | From BusyCoq Require Import Individual62. | 29 | From BusyCoq Require Import Individual62. |
| 19 | Require Import Arith Lia List. | 30 | Require Import Arith Lia List. |
| 20 | Require Import String. | 31 | Require Import String. |
| 21 | Import ListNotations. | 32 | Import ListNotations. |
| 23 | Definition tm := Eval compute in (TM_from_str "1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB---"). | 34 | Definition tm := Eval compute in (TM_from_str "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---"). |
| 25 | Notation "c -->* c'" := (c -[ tm ]->* c') (at level 40). | ||
| 36 | (** The parent machine (verify/Skelet1LikeC2_1RB0LD.v). Everything up to [nonhalt_D] is about [tm3]. *) | ||
| 26 | Notation "c -->+ c'" := (c -[ tm ]->+ c') (at level 40). | ||
| 37 | Definition tm3 := Eval compute in (TM_from_str "1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB---"). | ||
| 39 | Notation "c -->* c'" := (c -[ tm3 ]->* c') (at level 40). | ||
| 40 | Notation "c -->+ c'" := (c -[ tm3 ]->+ c') (at level 40). | ||
| 28 | Open Scope list. | 42 | Open Scope list. |
| 30 | Lemma ev_eq {c1 c2 c2'} : c1 -->* c2 -> c2 = c2' -> c1 -->* c2'. | 44 | Lemma ev_eq {c1 c2 c2'} : c1 -->* c2 -> c2 = c2' -> c1 -->* c2'. |
| ⋯ 258 identical lines (template 31–338, ours 45–352) | |||
| 339 | cbn [RP sd]. rewrite ovpX_eq. replace (pb+4) with (S (pb+3)) by lia. rewrite tailB_eq. reflexivity. | 353 | cbn [RP sd]. rewrite ovpX_eq. replace (pb+4) with (S (pb+3)) by lia. rewrite tailB_eq. reflexivity. |
| 340 | Qed. | 354 | Qed. |
| 342 | (** * Start (proof.md 3.7): c0 reaches K0 = K(2; (11,11,0); -) in 956 steps, and the base | ||
| 356 | (** * Start (proof.md 3.7, twin column). The twin from c0 corresponds to the parent [tm3] | ||
| 343 | E-start after overflow 6, K(2; (95,68,0),(34,33,1),(10,15,1),(1,24,1); -), in 78,710 steps. | ||
| 357 | from (D;; tape0), step for step. That run reaches K0' = K(2; (11,12,0); -) in 1,021 steps, | ||
| 344 | Both by direct execution ([esx]); the second takes about 30 s. *) | ||
| 358 | and the base E-start after overflow 6, K(2; (95,68,0),(34,33,1),(10,15,1),(1,25,1); -), in | ||
| 346 | Lemma init0 : c0 -->* K 2 [(11%nat, 11%nat, false)] TN. | ||
| 359 | 78,911 steps. Both by direct execution. [esx] runs its fast [vm_compute] path only from c0 | ||
| 347 | Proof. unfold K. cbn [RP RT sd]. esx. Qed. | ||
| 360 | (from another start it falls back to symbolic [es], far too slow here), so [solve_initD] is | ||
| 361 | busycoq's [solve_init] with the start config rewritten to [cconfig_to_config (nil,nil,0,D)]. *) | ||
| 363 | Ltac solve_initD := | ||
| 364 | change (D, tape0) with (cconfig_to_config (nil,nil,0,D)); | ||
| 365 | repeat rewrite Str_cons_def; | ||
| 366 | repeat rewrite <-Str_app_assoc; | ||
| 367 | repeat rewrite simpl_directed_head_l; | ||
| 368 | repeat rewrite simpl_directed_head_r; | ||
| 369 | repeat rewrite l_const0_app_nil; | ||
| 370 | repeat rewrite r_const0_app_nil; | ||
| 371 | repeat rewrite config_to_cconfig; | ||
| 372 | apply cconfig_evstep_dec_spec with (n:=1000000); | ||
| 373 | vm_compute; | ||
| 374 | reflexivity. | ||
| 376 | Lemma init0 : D;; tape0 -->* K 2 [(11%nat, 12%nat, false)] TN. | ||
| 377 | Proof. unfold K. cbn [RP RT sd]. solve_initD. Qed. | ||
| 349 | Definition base : list (nat*nat*bool) := | 379 | Definition base : list (nat*nat*bool) := |
| 350 | [(95%nat, 68%nat, false); (34%nat, 33%nat, true); (10%nat, 15%nat, true); (1%nat, 24%nat, true)]. | 380 | [(95%nat, 68%nat, false); (34%nat, 33%nat, true); (10%nat, 15%nat, true); (1%nat, 25%nat, true)]. |
| 352 | Lemma init : c0 -->* K 2 base TN. | 382 | Lemma init : D;; tape0 -->* K 2 base TN. |
| 353 | Proof. unfold K, base. cbn [RP RT sd]. esx. Qed. | 383 | Proof. unfold K, base. cbn [RP RT sd]. solve_initD. Qed. |
| 356 | (** * The invariant (round 2). Arithmetic layer, then the step lemma. *) | 386 | (** * The invariant (round 2). Arithmetic layer, then the step lemma. *) |
| 358 | Require Import ZifyNat. | 388 | Require Import ZifyNat. |
| ⋯ 814 identical lines (template 359–1264, ours 389–1294) | |||
| 1265 | cbn [AllI]. unfold PCx, Lift, PC, PN, PI. cbn. repeat split; lia. | 1295 | cbn [AllI]. unfold PCx, Lift, PC, PN, PI. cbn. repeat split; lia. |
| 1266 | Qed. | 1296 | Qed. |
| 1268 | Lemma nonhalt : ~ halts tm c0. | ||
| 1298 | (** The parent never halts from 0^inf D> 0^inf. *) | ||
| 1299 | Lemma nonhalt_D : ~ halts tm3 (D;; tape0). | ||
| 1269 | Proof. | 1300 | Proof. |
| 1270 | apply multistep_nonhalt with (c' := K 2 base TN); [exact init|]. | 1301 | apply multistep_nonhalt with (c' := K 2 base TN); [exact init|]. |
| 1271 | change (K 2 base TN) with (Cf (mkst 2 base TN E1 false)). | 1302 | change (K 2 base TN) with (Cf (mkst 2 base TN E1 false)). |
| 1272 | apply progress_nonhalt_cond with (P := J); [exact Jstep | exact J_base]. | 1303 | apply progress_nonhalt_cond with (P := J); [exact Jstep | exact J_base]. |
| 1273 | Qed. | 1304 | Qed. |
| 1306 | (** * Conjugacy (proof.md section 0, Lemma C). | ||
| 1307 | [flip tm] is the twin with every direction flipped (busycoq Flip.v); renaming its states | ||
| 1308 | by phi gives the parent exactly ([Perm], busycoq Permute.v: both the halting entry and | ||
| 1309 | all 11 transitions). [flip_halts]: halts tm c -> halts (flip tm) (flip_conf c), and | ||
| 1310 | flip_conf c0 = A;; tape0 (the blank tape is symmetric). [perm_halts]: halts (flip tm) | ||
| 1311 | (q;; t) -> halts tm3 (phi q;; t), and phi A = D. *) | ||
| 1313 | Definition phi (q : Q) : Q := | ||
| 1314 | match q with A => D | B => A | C => B | D => C | E => E | F => F end. | ||
| 1316 | Lemma perm_twin : Perm (flip tm) tm3 phi. | ||
| 1317 | Proof. | ||
| 1318 | split. | ||
| 1319 | - intros [] [] H; cbn in *; try discriminate; reflexivity. | ||
| 1320 | - intros [] [] s' d q' H; cbn in *; inversion H; subst; reflexivity. | ||
| 1321 | Qed. | ||
| 1323 | Lemma nonhalt: ~halts tm c0. | ||
| 1324 | Proof. | ||
| 1325 | intros H. apply flip_halts in H. | ||
| 1326 | change (halts (flip tm) (A;; tape0)) in H. | ||
| 1327 | exact (nonhalt_D (perm_halts _ _ _ _ _ perm_twin H)). | ||
| 1328 | Qed. | ||
| 1275 | (* | 1330 | (* |
| 1276 | ``` | 1331 | ``` |
| 1277 | 1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB--- | ||
| 1332 | 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC--- (= mirror of 1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB--- renamed by | ||
| 1333 | phi: A->D, B->A, C->B, D->C, E->E, F->F; | ||
| 1334 | tm3 below = the parent) | ||
| 1336 | twin c0 = 0^inf A> 0^inf <-> parent 0^inf D> 0^inf (flip_halts, Perm (flip tm) tm3 phi, perm_halts) | ||
| 1338 | Parent family (tm3), unchanged from the parent's kill file verify/Skelet1LikeC2_1RB0LD.v: | ||
| 1279 | [p,q,d] := (10)^p (01)^q s(d), s(1) = 0001, s(0) = 0010 [RP] | 1339 | [p,q,d] := (10)^p (01)^q s(d), s(1) = 0001, s(0) = 0010 [RP] |
| 1280 | K(h; P; T) := 0^inf <A (10)^h 11001 [p_1,q_1,d_1] ... [p_L,q_L,d_L] T 0^inf [K] | 1340 | K(h; P; T) := 0^inf <A (10)^h 11001 [p_1,q_1,d_1] ... [p_L,q_L,d_L] T 0^inf [K] |
| 1281 | T in { -, (10)^t 1, (101)^2 (01)^k } [TN, TA t, TB k] | 1341 | T in { -, (10)^t 1, (101)^2 (01)^k } [TN, TA t, TB k] |
| 1282 | k := least j with d_j = 1; Z := pairs 1..k-1 (all d = 0, q >= 2) | 1342 | k := least j with d_j = 1; Z := pairs 1..k-1 (all d = 0, q >= 2) |
| 1283 | touch (p,q,d) := (p+1, q-1, 1-d) | 1343 | touch (p,q,d) := (p+1, q-1, 1-d) |
| 1344 | (on the twin's tape: K' = mirror image, 0^inf T^R [p_L,q_L,d_L]^R ... [p_1,q_1,d_1]^R 10011 (01)^h B> 0^inf) | ||
| 1285 | Dec K(h; Z ++ (p,q+2,1) :: R; T) -->+ K(h+4; touch Z ++ (p+1,q+1,0) :: R; T) | 1346 | Dec K(h; Z ++ (p,q+2,1) :: R; T) -->+ K(h+4; touch Z ++ (p+1,q+1,0) :: R; T) |
| 1286 | DecMerge K(h; Z ++ (p,1,1) :: (p',q',d') :: R; T) -->+ K(h+4; touch Z ++ (p+p'+3,q',d') :: R; T) | 1347 | DecMerge K(h; Z ++ (p,1,1) :: (p',q',d') :: R; T) -->+ K(h+4; touch Z ++ (p+p'+3,q',d') :: R; T) |
| ⋯ 12 identical lines (template 1287–1298, ours 1348–1359) | |||
| 1299 | invariant J (per pair, n = pairs to the right, tv = digit value from the pair up, | 1360 | invariant J (per pair, n = pairs to the right, tv = digit value from the pair up, |
| 1300 | Rt = tv + phase term): see Definitions PN, PI, TC, J; preserved by every rule (Jstep). | 1361 | Rt = tv + phase term): see Definitions PN, PI, TC, J; preserved by every rule (Jstep). |
| 1301 | start: c0 -->(956) K(2; (11,11,0); -) -->(77,754) K(2; (95,68,0),(34,33,1),(10,15,1),(1,24,1); -) | 1362 | start (tm3): 0^inf D> 0^inf -->(1,021) K(2; (11,12,0); -) -->(77,890) K(2; (95,68,0),(34,33,1),(10,15,1),(1,25,1); -) |
| 1302 | ``` | 1363 | ``` |
| 1303 | *) | 1364 | *) |
4Proof outlineCheck: the new items (green) carry the argument; the names read like the proof.md rules.
142 items in 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---.v (1364 lines): 104 Lemma, 27 Definition, 8 Fixpoint, 2 Inductive, 1 Record. Tags against the template: identical = same name and same text once each file's own TM string is <TM> (marked "except the TM string" when that is the only difference); adapted = same name, different text; new = no item of that name in the template part.
| # | kind | name | statement (no proof body) | line | vs template |
|---|---|---|---|---|---|
| 1 | Definition | tm | Definition tm := Eval compute in (TM_from_str "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---"). | L34 | identicalexcept the TM string |
| 2 | Definition | tm3 | Definition tm3 := Eval compute in (TM_from_str "1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB---"). | L37 | new |
| 3 | Lemma | ev_eq | Lemma ev_eq {c1 c2 c2'} : c1 -->* c2 -> c2 = c2' -> c1 -->* c2'. | L44 | identical |
| 4 | Lemma | prog_eq | Lemma prog_eq {c1 c2 c2'} : c1 -->+ c2 -> c2 = c2' -> c1 -->+ c2'. | L47 | identical |
| 5 | Lemma | Start | Lemma Start h r : 0inf <{{A}} [1;0]^^h *> [1;1;0;0;1] *> r -->+
0inf <* <[1;0]^^(4+h) <* <[1;1;1] <* [0] {{B}}> r. | L55 | identical |
| 6 | Lemma | PassR | Lemma PassR l p q r : l <* [0] {{B}}> [1;0]^^p *> [0;1]^^(S q) *> [0;0;1;0] *> r -->*
l <* [0] <* <[0;1]^^p <* <[1;1;0] <* <[0;1]^^q <* <[1;1] <* [0] {{B}}> r. | L59 | identical |
| 7 | Lemma | Borrow | Lemma Borrow l p q r : l {{B}}> [1;0]^^p *> [0;1]^^(S (S q)) *> [0;0;0;1] *> r -->*
l <{{D}} [1;0]^^(S p) *> [0;1]^^(S q) *> [0;0;1;0] *> r. | L63 | identical |
| 8 | Lemma | PassL | Lemma PassL l p q r : l <* [0] <* <[0;1]^^p <* <[1;1;0] <* <[0;1]^^(S q) <* <[1;1] <* [0] <{{D}} r -->*
l <* [0] <{{D}} [1;0]^^(S p) *> [0;1]^^(S q) *> [0;0;0;1] *> r. | L67 | identical |
| 9 | Lemma | EndPh | Lemma EndPh h r : 0inf <* <[1;0]^^(4+h) <* <[1;1;1] <* [0] <{{D}} r -->*
0inf <{{A}} [1;0]^^(4+h) *> [1;1;0;0;1] *> r. | L71 | identical |
| 10 | Lemma | EndT | Lemma EndT l p q : l <* <[0;1]^^p <* <[1;1;0] <* <[0;1]^^(S q) <* <[1;1] <* [0] {{B}}> 0inf -->*
l <{{D}} [1;0]^^(S p) *> [0;1]^^(S q) *> [0;0;1;0] *> [1;0;1] *> 0inf. | L75 | identical |
| 11 | Lemma | EndLastT | Lemma EndLastT l p : l <* <[0;1]^^p <* <[1;1;0] <* <[1;1] <* [0] {{B}}> 0inf -->*
l <{{D}} [1;0]^^(p+4) *> [1] *> 0inf. | L79 | identical |
| 12 | Lemma | MergeB | Lemma MergeB l p p' r : l {{B}}> [1;0]^^p *> [0;1] *> [0;0;0;1] *> [1;0]^^p' *> r -->*
l <{{D}} [1;0]^^(p+p'+3) *> r. | L83 | identical |
| 13 | Lemma | MergeE | Lemma MergeE l p : l {{B}}> [1;0]^^p *> [0;1] *> [0;0;0;1] *> 0inf -->*
l <{{D}} [1;0]^^(p+2) *> [1] *> 0inf. | L87 | identical |
| 14 | Lemma | OvT | Lemma OvT l t : l <* [0] {{B}}> [1;0]^^t *> [1] *> 0inf -->*
l <{{D}} [0;1]^^(S t) *> [0;0;0;1] *> 0inf. | L91 | identical |
| 15 | Lemma | OvL | Lemma OvL l p q r : l <* [0] <* <[0;1]^^(S p) <* <[1;1;0] <* <[0;1]^^q <* <[1;1] <{{D}} r -->*
l <{{D}} [0;1]^^(S p) *> [0;0;0;1] *> [1;0]^^(S q) *> r. | L95 | identical |
| 16 | Lemma | OvEnd | Lemma OvEnd h p r : 0inf <* <[1;0]^^(4+h) <* <[1;1;1] <{{D}} [0;1]^^(S (S p)) *> [0;0;0;1] *> r -->*
0inf <{{A}} [1;0]^^2 *> [1;1;0;0;1] *> [1;0]^^(h+5) *> [0;1]^^(S p) *> [0;0;1;0] *> r. | L99 | identical |
| 17 | Lemma | X1Sw | Lemma X1Sw l p r : l <* [0] <* <[0;1]^^(S p) <* <[1;1;0] <* <[1;1] <* [0] <{{D}} r -->*
l <{{D}} [0;1]^^(S p) *> [0;0;1;0;1;0;1] *> r. | L103 | identical |
| 18 | Lemma | X2T | Lemma X2T l p q k : l <* <[0;1]^^p <* <[1;1;0] <* <[0;1]^^(S q) <* <[1;1] <* [0] {{B}}> [1;0;1;1;0;1] *> [0;1]^^(S k) *> 0inf -->*
l <{{D}} [1;0]^^(S p) *> [0;1]^^(S q) *> [0;0;1;0] *> [1;0]^^3 *> [0;1]^^(S k) *> [0;0;0;1] *> 0inf. | L107 | identical |
| 19 | Definition | sd | Definition sd (d : bool) : list Sym := if d then [0;0;0;1] else [0;0;1;0]. | L113 | identical |
| 20 | Fixpoint | RP | Fixpoint RP (P : list (nat*nat*bool)) (r : side) : side := match P with | [] => r | (p,q,d) :: P' => [1;0]^^p *> [0;1]^^q *> sd d *> RP P' r end. | L115 | identical |
| 21 | Inductive | Tl | Inductive Tl := TN | TA (t : nat) | TB (k : nat). | L121 | identical |
| 22 | Definition | RT | Definition RT (T : Tl) : side := match T with | TN => 0inf | TA t => [1;0]^^t *> [1] *> 0inf | TB k => [1;0;1;1;0;1] *> [0;1]^^k *> 0inf end. | L123 | identical |
| 23 | Definition | K | Definition K (h : nat) (P : list (nat*nat*bool)) (T : Tl) : Q * tape :=
0inf <{{A}} [1;0]^^h *> [1;1;0;0;1] *> RP P (RT T). | L130 | identical |
| 24 | Definition | pre | Definition pre (h : nat) : side := 0inf <* <[1;0]^^(4+h) <* <[1;1;1]. | L133 | identical |
| 25 | Definition | reg | Definition reg (p q : nat) (l : side) : side := l <* [0] <* <[0;1]^^p <* <[1;1;0] <* <[0;1]^^(pred q) <* <[1;1]. | L136 | identical |
| 26 | Fixpoint | LP | Fixpoint LP (Z : list (nat*nat*bool)) (l : side) : side := match Z with | [] => l | (p,q,d) :: Z' => LP Z' (reg p q l) end. | L139 | identical |
| 27 | Fixpoint | OvR | Fixpoint OvR (Z : list (nat*nat*bool)) (r : side) : side := match Z with | [] => r | (p,q,d) :: Z' => [0;1]^^p *> [0;0;0;1] *> [1;0]^^q *> OvR Z' r end. | L146 | identical |
| 28 | Definition | touch | Definition touch (x : nat*nat*bool) : nat*nat*bool := let '(p,q,d) := x in (S p, pred q, negb d). | L152 | identical |
| 29 | Definition | okR | Definition okR (x : nat*nat*bool) : Prop := let '(p,q,d) := x in d = false /\ 1 <= q. | L155 | identical |
| 30 | Definition | okL | Definition okL (x : nat*nat*bool) : Prop := let '(p,q,d) := x in d = false /\ 2 <= q. | L156 | identical |
| 31 | Definition | okO | Definition okO (x : nat*nat*bool) : Prop := let '(p,q,d) := x in 1 <= p /\ 1 <= q. | L157 | identical |
| 32 | Lemma | RP_app | Lemma RP_app Z W r : RP (Z ++ W) r = RP Z (RP W r). | L159 | identical |
| 33 | Lemma | LP_app | Lemma LP_app Z W l : LP (Z ++ W) l = LP W (LP Z l). | L164 | identical |
| 34 | Lemma | PassesR | Lemma PassesR Z : Forall okR Z -> forall l r,
l <* [0] {{B}}> RP Z r -->* LP Z l <* [0] {{B}}> r. | L169 | identical |
| 35 | Lemma | PassesL | Lemma PassesL Z : Forall okL Z -> forall l r,
LP Z l <* [0] <{{D}} r -->* l <* [0] <{{D}} RP (map touch Z) r. | L179 | identical |
| 36 | Lemma | OvPasses | Lemma OvPasses Z : Forall okO Z -> forall l r,
LP Z l <{{D}} r -->* l <{{D}} OvR Z r. | L189 | identical |
| 37 | Lemma | okL_R | Lemma okL_R Z : Forall okL Z -> Forall okR Z. | L199 | identical |
| 38 | Lemma | Dec | Lemma Dec h Z p q R T : Forall okL Z -> K h (Z ++ (p, S (S q), true) :: R) T -->+ K (4+h) (map touch Z ++ (S p, S q, false) :: R) T. | L206 | identical |
| 39 | Lemma | DecMerge | Lemma DecMerge h Z p p' q' d' R T : Forall okL Z -> K h (Z ++ (p, 1%nat, true) :: (p', q', d') :: R) T -->+ K (4+h) (map touch Z ++ (p+p'+3, q', d') :: R) T. | L217 | identical |
| 40 | Lemma | DecMergeTail | Lemma DecMergeTail h Z p t : Forall okL Z -> K h (Z ++ [(p, 1%nat, true)]) (TA t) -->+ K (4+h) (map touch Z) (TA (p+t+3)). | L228 | identical |
| 41 | Lemma | DecMergeEmpty | Lemma DecMergeEmpty h Z p : Forall okL Z -> K h (Z ++ [(p, 1%nat, true)]) TN -->+ K (4+h) (map touch Z) (TA (p+2)). | L239 | identical |
| 42 | Lemma | Forall_snoc | Lemma Forall_snoc {A} (P : A -> Prop) Z x : Forall P Z -> P x -> Forall P (Z ++ [x]). | L250 | identical |
| 43 | Lemma | EndR | Lemma EndR h Z p q : Forall okL Z -> K h (Z ++ [(p, S (S q), false)]) TN -->+ K (4+h) (map touch Z ++ [(S p, S q, false)]) (TA 1). | L253 | identical |
| 44 | Lemma | EndLast | Lemma EndLast h Z p : Forall okL Z -> K h (Z ++ [(p, 1%nat, false)]) TN -->+ K (4+h) (map touch Z) (TA (p+4)). | L265 | identical |
| 45 | Lemma | X2 | Lemma X2 h Z p q k : Forall okL Z -> K h (Z ++ [(p, S (S q), false)]) (TB (S k)) -->+ K (4+h) (map touch Z ++ [(S p, S q, false); (3%nat, S k, true)]) TN. | L277 | identical |
| 46 | Fixpoint | ovp | Fixpoint ovp (q : nat) (Z : list (nat*nat*bool)) (t : nat) : list (nat*nat*bool) := match Z with | [] => [(q, S t, true)] | (p',q',_) :: Z' => (q, p', true) :: ovp q' Z' t end. | L290 | identical |
| 47 | Lemma | ovp_eq | Lemma ovp_eq Z : forall q t, RP (ovp q Z t) 0inf = [1;0]^^q *> OvR Z ([0;1]^^(S t) *> [0;0;0;1] *> 0inf). | L296 | identical |
| 48 | Lemma | Ov | Lemma Ov h p1 q1 Z t : 1 <= q1 -> Forall okR Z -> Forall okO Z -> K h ((S (S p1), q1, false) :: Z) (TA t) -->+ K 2 ((h+5, S p1, false) :: ovp q1 Z t) TN. | L302 | identical |
| 49 | Fixpoint | ovpX | Fixpoint ovpX (q : nat) (Z : list (nat*nat*bool)) (pa : nat) : list (nat*nat*bool) := match Z with | [] => [(q, pa, false)] | (p',q',_) :: Z' => (q, p', true) :: ovpX q' Z' pa end. | L317 | identical |
| 50 | Lemma | ovpX_eq | Lemma ovpX_eq Z : forall q pa r, RP (ovpX q Z pa) r = [1;0]^^q *> OvR Z ([0;1]^^pa *> [0;0;1;0] *> r). | L323 | identical |
| 51 | Lemma | tailB_eq | Lemma tailB_eq n : [0;0;1;0;1;0;1] *> [1;0]^^(S n) *> [1] *> 0inf = [0;0;1;0] *> RT (TB n). | L329 | identical |
| 52 | Lemma | X1 | Lemma X1 h p1 q1 Z pa pb : 1 <= q1 -> Forall okR Z -> Forall okO Z -> K h ((S (S p1), q1, false) :: Z ++ [(S pa, 1%nat, false); (pb, 1%nat, false)]) TN -->+ K 2 ((h+5, S p1, false) :: ovpX q1 Z (S pa)) (TB (pb+3)). | L337 | identical |
| 53 | Lemma | init0 | Lemma init0 : D;; tape0 -->* K 2 [(11%nat, 12%nat, false)] TN. | L376 | adapted |
| 54 | Definition | base | Definition base : list (nat*nat*bool) := [(95%nat, 68%nat, false); (34%nat, 33%nat, true); (10%nat, 15%nat, true); (1%nat, 25%nat, true)]. | L379 | adapted |
| 55 | Lemma | init | Lemma init : D;; tape0 -->* K 2 base TN. | L382 | adapted |
| 56 | Definition | bv | Definition bv (d : bool) : nat := if d then 1 else 0. | L394 | identical |
| 57 | Fixpoint | dv | Fixpoint dv (P : list tri) : nat := match P with | [] => 0 | (_,_,d) :: P' => bv d + 2 * dv P' end. | L396 | identical |
| 58 | Definition | dig | Definition dig (x : tri) : bool := let '(_,_,d) := x in d. | L402 | identical |
| 59 | Definition | dig0 | Definition dig0 (x : tri) : Prop := dig x = false. | L403 | identical |
| 60 | Lemma | dv_lt | Lemma dv_lt P : dv P < 2 ^ length P. | L407 | identical |
| 61 | Lemma | dv_zeros | Lemma dv_zeros Z R : Forall dig0 Z -> dv (Z ++ R) = 2 ^ length Z * dv R. | L413 | identical |
| 62 | Lemma | dv_tz | Lemma dv_tz Z R : Forall dig0 Z -> dv (map touch Z ++ R) + 1 = 2 ^ length Z + 2 ^ length Z * dv R. | L420 | identical |
| 63 | Fixpoint | AllI | Fixpoint AllI (Pr : nat -> tri -> list tri -> Prop) (i : nat) (P : list tri) : Prop := match P with | [] => True | x :: Y => Pr i x Y /\ AllI Pr (S i) Y end. | L428 | identical |
| 64 | Lemma | AllI_app | Lemma AllI_app Pr Z : forall i R, AllI Pr i (Z ++ R) -> AllI Pr (i + length Z) R. | L434 | identical |
| 65 | Lemma | AllI_mono | Lemma AllI_mono (Pr Pr' : nat -> tri -> list tri -> Prop) P : forall i, (forall j x Y, i <= j -> Pr j x Y -> Pr' j x Y) -> AllI Pr i P -> AllI Pr' i P. | L441 | identical |
| 66 | Lemma | AllI_shift | Lemma AllI_shift (Pr Pr' : nat -> tri -> list tri -> Prop) P : forall i, (forall j x Y, i <= j -> Pr (S j) x Y -> Pr' j x Y) -> AllI Pr (S i) P -> AllI Pr' i P. | L449 | identical |
| 67 | Lemma | AllI_touchZ | Lemma AllI_touchZ (Pr Pr' : nat -> tri -> list tri -> Prop) R R' : forall Z i, Forall dig0 Z -> (forall j p q Zr, Forall dig0 Zr -> j + S (length Zr) = i + length Z -> Pr j (p,q,false) (Zr ++ R) -> Pr' j (S p, pred q, true) (map touch Zr ++ R')) -> AllI Pr i (Z ++ R) -> AllI Pr' (i + length Z) R' -> AllI Pr' i (map touch Z ++ R'). | L458 | identical |
| 68 | Inductive | phase | Inductive phase := E1 | E2 | E1t | E2t | T0 | L1 | L2 | LX. | L479 | identical |
| 69 | Definition | PN | Definition PN (ph : phase) (c4 : bool) (p q n tv : nat) : Prop :=
match ph with
| E1 => match n with
| 0 => q >= tv + 2 ^ n + 1 /\ p + tv + 2 ^ n >= 3
| S _ => q >= tv + 3 * 2 ^ n + 1 /\ (p + tv) mod 2 = 1 /\ p + tv + 2 ^ n >= 3 * 2 ^ n
end
… +35 lines | L482 | identical |
| 70 | Definition | PI | Definition PI (ph : phase) (h i p q n tv : nat) : Prop :=
match i with
| 1 => h mod 2 = 0 /\
match ph with
| E1 | E1t => 2 <= n /\ p + tv + 2 ^ n + 3 >= 11 * 2 ^ n /\ h + 4 * (tv + 2 ^ n) + 6 >= 12 * 2 ^ n
| E2 | E2t => 2 <= n /\ p + tv + 3 >= 11 * 2 ^ n /\ h + 4 * tv + 6 >= 12 * 2 ^ n
… +14 lines | L525 | identical |
| 71 | Definition | PC | Definition PC (ph : phase) (c4 : bool) (h i p q n tv : nat) : Prop := 1 <= p /\ 1 <= q /\ PN ph c4 p q n tv /\ PI ph h i p q n tv. | L546 | identical |
| 72 | Definition | Lift | Definition Lift (Pr : nat -> nat -> nat -> nat -> nat -> Prop) (i : nat) (x : tri) (Y : list tri) : Prop := let '(p,q,d) := x in Pr i p q (length Y) (dv (x :: Y)). | L549 | identical |
| 73 | Definition | PCx | Definition PCx (ph : phase) (c4 : bool) (h : nat) := Lift (PC ph c4 h). | L552 | identical |
| 74 | Lemma | pow_pos | Lemma pow_pos n : 1 <= 2 ^ n. | L561 | identical |
| 75 | Lemma | ob_touch | Lemma ob_touch ph c4 h i p q n tv : 1 <= tv -> 2 <= q -> PC ph c4 h i p q n tv -> PC ph c4 (4 + h) i (S p) (pred q) n (tv - 1). | L565 | identical |
| 76 | Lemma | pow_S | Lemma pow_S n : 2 ^ S n = 2 * 2 ^ n. | L573 | identical |
| 77 | Lemma | ob_merge | Lemma ob_merge ph c4 h i p q n u U : (ph = L1 \/ ph = L2 \/ ph = LX) -> 1 <= n -> 2 <= u -> u mod 2 = 0 -> U mod 2 = 0 -> U + u <= 2 * 2 ^ n -> (ph = L1 -> U + u <= 2 ^ n) -> (ph = LX -> 2 <= n) -> (ph = L1 -> c4 = true -> 2 <= n) -> (i = 1 -> 2 <= n) -> (ph = LX -> i = 1 -> 3 <= n) -> 2 <= q -> PC ph c4 h i p q (S n) (u + 2 * U) -> PC ph c4 (4 + h) i (S p) (pred q) n (u - 1 + U). | L581 | identical |
| 78 | Lemma | ob_mt | Lemma ob_mt c4 h i p q n : 2 <= q -> (i = 1 -> 1 <= n) -> PC L2 c4 h i p q (S n) (2 * 2 ^ n) -> PC L2 false (4 + h) i (S p) (pred q) n (2 * 2 ^ n - 1). | L597 | identical |
| 79 | Lemma | ob_fuse | Lemma ob_fuse ph c4 h h' k p p' q' n tv : (ph = L1 \/ ph = L2 \/ ph = LX) -> 3 <= k -> PC ph c4 h (S k) p' q' n tv -> PC ph c4 h' k (p + p' + 3) q' n tv. | L606 | identical |
| 80 | Lemma | ob_far | Lemma ob_far ph c4 h h' i j p q n tv : 3 <= i -> 3 <= j -> PC ph c4 h i p q n tv -> PC ph c4 h' j p q n tv. | L615 | identical |
| 81 | Definition | endtr | Definition endtr (ph ph' : phase) : Prop := (ph = E1 /\ ph' = E2) \/ (ph = E1t /\ ph' = E2t). | L623 | identical |
| 82 | Lemma | ob_end | Lemma ob_end ph ph' h i p q n : endtr ph ph' -> 1 <= n -> 2 <= q -> PC ph false h i p q n 0 -> PC ph' false (4 + h) i (S p) (pred q) n (2 ^ n - 1). | L625 | identical |
| 83 | Lemma | ob_end_top | Lemma ob_end_top ph ph' h i p q : endtr ph ph' -> 3 <= i -> PC ph false h i p (S (S q)) 0 0 -> PC ph' false (4 + h) i (S p) (S q) 0 0. | L633 | identical |
| 84 | Lemma | ob_endlast | Lemma ob_endlast c4 h i p q n : 2 <= q -> PC L1 c4 h i p q (S n) 0 -> PC L2 c4 (4 + h) i (S p) (pred q) n (2 * 2 ^ n - 1). | L642 | identical |
| 85 | Lemma | ob_x2 | Lemma ob_x2 h i p q n : 1 <= n -> 2 <= q -> PC T0 false h i p q n 0 -> PC E1t false (4 + h) i (S p) (pred q) (S n) (3 * 2 ^ n - 1). | L651 | identical |
| 86 | Lemma | ob_x2_top | Lemma ob_x2_top h i p q : 3 <= i -> PC T0 false h i p (S (S q)) 0 0 -> PC E1t false (4 + h) i (S p) (S q) 1 2. | L659 | identical |
| 87 | Lemma | ob_x2_new | Lemma ob_x2_new h i k : 3 <= i -> 3 <= k -> PC E1t false h i 3 k 0 1. | L667 | identical |
| 88 | Definition | ovtr | Definition ovtr (ph ph' : phase) (c4' : bool) (Xp : nat -> Prop) : Prop := (ph = E2 /\ ph' = L1 /\ c4' = false /\ Xp = (fun x => x <> 4)) \/ (ph = E2 /\ ph' = LX /\ c4' = false /\ Xp = (fun x => x = 4)) \/ (ph = E2t /\ ph' = L1 /\ c4' = true /\ Xp = (fun _ => True)) \/ (ph = L2 /\ ph' = E1 /\ c4' = false /\ Xp = (fun _ => True)). | L675 | identical |
| 89 | Lemma | ob_ov_head | Lemma ob_ov_head ph ph' c4' Xp h p1 q1 n : ovtr ph ph' c4' Xp -> PC ph false h 1 (S (S p1)) q1 n 0 -> PC ph' c4' 2 1 (h + 5) (S p1) (S n) (2 * (2 * 2 ^ n) - 2). | L681 | identical |
| 90 | Lemma | ob_ov_step | Lemma ob_ov_step ph ph' c4' Xp h i pp q p' q' m : ovtr ph ph' c4' Xp -> 1 <= i -> PC ph false h i pp q (S m) 0 -> PC ph false h (S i) p' q' m 0 -> (m = 0 -> Xp p') -> PC ph' c4' 2 (S i) q p' (S m) (2 * (2 * 2 ^ m) - 1). | L693 | identical |
| 91 | Lemma | ob_ov_base | Lemma ob_ov_base ph ph' c4' Xp h i pp q t : ovtr ph ph' c4' Xp -> 1 <= i -> (ph = L2 -> 2 <= t) -> (ph <> L2 -> t = 1) -> PC ph false h i pp q 0 0 -> PC ph' c4' 2 (S i) q (S t) 0 1. | L709 | identical |
| 92 | Lemma | ob_x1_head | Lemma ob_x1_head h p1 q1 n : PC LX false h 1 (S (S p1)) q1 (S (S n)) 0 -> PC T0 false 2 1 (h + 5) (S p1) (S n) (2 * 2 ^ n - 2). | L721 | identical |
| 93 | Lemma | ob_x1_step | Lemma ob_x1_step h i pp q p' q' m : 1 <= i -> PC LX false h i pp q (S (S (S m))) 0 -> PC LX false h (S i) p' q' (S (S m)) 0 -> PC T0 false 2 (S i) q p' (S m) (2 * 2 ^ m - 1). | L728 | identical |
| 94 | Lemma | ob_x1_base | Lemma ob_x1_base h i pp q pa : 1 <= i -> PC LX false h i pp q 2 0 -> PC LX false h (S i) (S pa) 1 1 0 -> PC T0 false 2 (S i) q (S pa) 0 0. | L736 | identical |
| 95 | Lemma | dv_zero | Lemma dv_zero Z : Forall dig0 Z -> dv Z = 0. | L745 | identical |
| 96 | Lemma | dv_tz' | Lemma dv_tz' Z R : Forall dig0 Z -> dv (map touch Z ++ R) = 2 ^ length Z - 1 + 2 ^ length Z * dv R. | L748 | identical |
| 97 | Lemma | ovp_len | Lemma ovp_len q Z t : length (ovp q Z t) = S (length Z). | L751 | identical |
| 98 | Lemma | ovp_dv | Lemma ovp_dv q Z t : dv (ovp q Z t) + 1 = 2 ^ S (length Z). | L754 | identical |
| 99 | Lemma | ovpX_len | Lemma ovpX_len q Z pa : length (ovpX q Z pa) = S (length Z). | L760 | identical |
| 100 | Lemma | ovpX_dv | Lemma ovpX_dv q Z pa : dv (ovpX q Z pa) + 1 = 2 ^ length Z. | L763 | identical |
| 101 | Fixpoint | lastOK | Fixpoint lastOK (Xp : nat -> Prop) (Z : list tri) : Prop := match Z with | [] => True | [(p,_,_)] => Xp p | _ :: Z' => lastOK Xp Z' end. | L769 | identical |
| 102 | Lemma | lastOK_cons | Lemma lastOK_cons Xp p q d Z : lastOK Xp ((p,q,d) :: Z) -> (Z = [] -> Xp p) /\ lastOK Xp Z. | L776 | identical |
| 103 | Lemma | lastOK_dec | Lemma lastOK_dec Z : lastOK (fun x => x = 4) Z \/ lastOK (fun x => x <> 4) Z. | L779 | identical |
| 104 | Lemma | AllI_ovp | Lemma AllI_ovp ph ph' c4' Xp h t : ovtr ph ph' c4' Xp -> (ph = L2 -> 2 <= t) -> (ph <> L2 -> t = 1) -> forall Z i pp q, 1 <= i -> Forall dig0 Z -> lastOK Xp Z -> PC ph false h i pp q (length Z) 0 -> AllI (PCx ph false h) (S i) Z -> AllI (PCx ph' c4' 2) (S i) (ovp q Z t). | L785 | identical |
| 105 | Lemma | AllI_ovpX | Lemma AllI_ovpX h pa pb : forall Z i pp q, 1 <= i -> Forall dig0 Z -> PC LX false h i pp q (S (S (length Z))) 0 -> AllI (PCx LX false h) (S i) (Z ++ [(S pa, 1, false); (pb, 1, false)]) -> AllI (PCx T0 false 2) (S i) (ovpX q Z (S pa)). | L803 | identical |
| 106 | Lemma | passq | Lemma passq ph c4 h i p q n tv : PC ph c4 h i p q n tv -> 2 <= tv -> tv mod 2 = 0 -> 2 <= q. | L825 | identical |
| 107 | Lemma | Z_okL | Lemma Z_okL ph c4 h : forall Z i x R, Forall dig0 Z -> dig x = true -> AllI (PCx ph c4 h) i (Z ++ x :: R) -> Forall okL Z. | L831 | identical |
| 108 | Lemma | borrow1 | Lemma borrow1 ph c4 h k p n tv : 1 <= k -> tv mod 2 = 1 -> PC ph c4 h k p 1 n tv -> (ph = L1 \/ ph = L2 \/ ph = LX) /\ 3 <= k /\ (ph = L1 -> 1 <= n /\ tv + 1 <= 2 ^ n /\ (c4 = true -> 2 <= n)) /\ (ph = LX -> 2 <= n). | L844 | identical |
| 109 | Lemma | even2 | Lemma even2 x : (2 * x) mod 2 = 0. | L858 | identical |
| 110 | Lemma | pc_len | Lemma pc_len (Pr : nat -> tri -> list tri -> Prop) i P : AllI Pr i P -> True. | L861 | identical |
| 111 | Lemma | inv_Dec | Lemma inv_Dec ph c4 h Z p q R : Forall dig0 Z -> AllI (PCx ph c4 h) 1 (Z ++ (p, S (S q), true) :: R) -> AllI (PCx ph c4 (4 + h)) 1 (map touch Z ++ (S p, S q, false) :: R). | L867 | identical |
| 112 | Lemma | snoc_nn | Lemma snoc_nn (Z : list tri) y : Z ++ [y] <> []. | L888 | identical |
| 113 | Definition | minlen | Definition minlen (ph : phase) : nat := match ph with LX => 3 | L2 => 1 | _ => 2 end. | L891 | identical |
| 114 | Lemma | head_len | Lemma head_len ph c4 h x Y : PCx ph c4 h 1 x Y -> minlen ph <= length Y. | L893 | identical |
| 115 | Lemma | AllI_len | Lemma AllI_len ph c4 h P : P <> [] -> AllI (PCx ph c4 h) 1 P -> S (minlen ph) <= length P. | L899 | identical |
| 116 | Lemma | q2_V0 | Lemma q2_V0 ph c4 h i p q n : PC ph c4 h i p q n 0 -> 1 <= n -> (ph = LX -> 2 <= n) -> 2 <= q. | L904 | identical |
| 117 | Lemma | p1_V0 | Lemma p1_V0 ph c4 h p q n : PC ph c4 h 1 p q n 0 -> (ph = E2 \/ ph = E2t \/ ph = L2 \/ ph = LX) -> 2 <= p. | L910 | identical |
| 118 | Lemma | L2_c4_V0 | Lemma L2_c4_V0 h i p q : PC L2 true h i p q 0 0 -> False. | L916 | identical |
| 119 | Lemma | AllI_okRO | Lemma AllI_okRO ph c4 h : forall Z i, Forall dig0 Z -> AllI (PCx ph c4 h) i Z -> Forall okR Z /\ Forall okO Z. | L919 | identical |
| 120 | Lemma | inv_Merge | Lemma inv_Merge ph c4 h Z p p' q' d' R0 : Forall dig0 Z -> AllI (PCx ph c4 h) 1 (Z ++ (p, 1, true) :: (p', q', d') :: R0) -> AllI (PCx ph c4 (4 + h)) 1 (map touch Z ++ (p + p' + 3, q', d') :: R0). | L927 | identical |
| 121 | Lemma | inv_MT | Lemma inv_MT c4 h Z p : Forall dig0 Z -> AllI (PCx L2 c4 h) 1 (Z ++ [(p, 1, true)]) -> AllI (PCx L2 false (4 + h)) 1 (map touch Z) /\ 2 <= length Z. | L970 | identical |
| 122 | Lemma | inv_End | Lemma inv_End ph ph' h Z p q : endtr ph ph' -> Forall dig0 Z -> AllI (PCx ph false h) 1 (Z ++ [(p, S (S q), false)]) -> AllI (PCx ph' false (4 + h)) 1 (map touch Z ++ [(S p, S q, false)]). | L988 | identical |
| 123 | Lemma | inv_X2 | Lemma inv_X2 h Z p q k : Forall dig0 Z -> 3 <= k -> AllI (PCx T0 false h) 1 (Z ++ [(p, S (S q), false)]) -> AllI (PCx E1t false (4 + h)) 1 (map touch Z ++ [(S p, S q, false); (3, k, true)]). | L1010 | identical |
| 124 | Lemma | inv_EndLast | Lemma inv_EndLast c4 h Z p : Forall dig0 Z -> AllI (PCx L1 c4 h) 1 (Z ++ [(p, 1, false)]) -> AllI (PCx L2 c4 (4 + h)) 1 (map touch Z) /\ 2 <= length Z. | L1033 | identical |
| 125 | Lemma | inv_Ov | Lemma inv_Ov ph ph' c4' Xp h p1 q1 Z t : ovtr ph ph' c4' Xp -> (ph = L2 -> 2 <= t) -> (ph <> L2 -> t = 1) -> Forall dig0 Z -> lastOK Xp Z -> AllI (PCx ph false h) 1 ((S (S p1), q1, false) :: Z) -> AllI (PCx ph' c4' 2) 1 ((h + 5, S p1, false) :: ovp q1 Z t). | L1050 | identical |
| 126 | Lemma | inv_X1 | Lemma inv_X1 h p1 q1 Z pa pb : Forall dig0 Z -> AllI (PCx LX false h) 1 ((S (S p1), q1, false) :: Z ++ [(S pa, 1, false); (pb, 1, false)]) -> AllI (PCx T0 false 2) 1 ((h + 5, S p1, false) :: ovpX q1 Z (S pa)). | L1065 | identical |
| 127 | Record | st | Record st := mkst { sh : nat; sP : list (nat*nat*bool); sT : Tl; sph : phase; sc4 : bool }. | L1084 | identical |
| 128 | Definition | Cf | Definition Cf (s : st) : Q * tape := K (sh s) (sP s) (sT s). | L1086 | identical |
| 129 | Definition | TC | Definition TC (ph : phase) (c4 : bool) (T : Tl) : Prop := match ph with | E1 | E1t | LX => T = TN /\ c4 = false | L1 => T = TN | E2 | E2t => T = TA 1 /\ c4 = false | T0 => (exists k, T = TB k /\ 3 <= k) /\ c4 = false … +2 lines | L1088 | identical |
| 130 | Definition | J | Definition J (s : st) : Prop := sP s <> [] /\ TC (sph s) (sc4 s) (sT s) /\ AllI (PCx (sph s) (sc4 s) (sh s)) 1 (sP s). | L1097 | identical |
| 131 | Lemma | split1 | Lemma split1 (P : list tri) : (exists Z x R, P = Z ++ x :: R /\ Forall dig0 Z /\ dig x = true) \/ Forall dig0 P. | L1100 | identical |
| 132 | Lemma | Z_okL_V0 | Lemma Z_okL_V0 ph c4 h y : ph <> LX -> forall Z i, Forall dig0 (Z ++ [y]) -> AllI (PCx ph c4 h) i (Z ++ [y]) -> Forall okL Z. | L1112 | identical |
| 133 | Lemma | lastOK_True | Lemma lastOK_True Z : lastOK (fun _ => True) Z. | L1122 | identical |
| 134 | Lemma | Forall_snoc_inv | Lemma Forall_snoc_inv (Pr : tri -> Prop) Z y : Forall Pr (Z ++ [y]) -> Forall Pr Z /\ Pr y. | L1125 | identical |
| 135 | Lemma | last_pc | Lemma last_pc ph c4 h Z p q d : Forall dig0 (Z ++ [(p,q,d)]) -> AllI (PCx ph c4 h) 1 (Z ++ [(p,q,d)]) -> d = false /\ PC ph c4 h (1 + length Z) p q 0 0. | L1128 | identical |
| 136 | Lemma | first_pc | Lemma first_pc ph c4 h p q d Z : Forall dig0 ((p,q,d) :: Z) -> AllI (PCx ph c4 h) 1 ((p,q,d) :: Z) -> d = false /\ PC ph c4 h 1 p q (length Z) 0 /\ Forall dig0 Z /\ AllI (PCx ph c4 h) 2 Z. | L1136 | identical |
| 137 | Lemma | Jstep | Lemma Jstep : forall s, J s -> exists s', Cf s -->+ Cf s' /\ J s'. | L1146 | identical |
| 138 | Lemma | J_base | Lemma J_base : J (mkst 2 base TN E1 false). | L1292 | identical |
| 139 | Lemma | nonhalt_D | Lemma nonhalt_D : ~ halts tm3 (D;; tape0). | L1299 | new |
| 140 | Definition | phi | Definition phi (q : Q) : Q := match q with A => D | B => A | C => B | D => C | E => E | F => F end. | L1313 | new |
| 141 | Lemma | perm_twin | Lemma perm_twin : Perm (flip tm) tm3 phi. | L1316 | new |
| 142 | Lemma | nonhalt | Lemma nonhalt: ~halts tm c0. | L1323 | adapted |
5What a maintainer readsCheck: the rule table below is what the .v proves, and proof.md / README read cleanly for a maintainer.
- submission/proof.md · informal proof (submitted copy)
- submission/README.md · the package README
- submission/discord.md · Discord draft (not posted)
- submission/parent-proof.md · the parent's proof, as shipped
- proof.md (working copy) · differs from the submitted copy
Every rule of parent §2 (Dec_k, DecMerge_k, DecMergeTail, DecMergeEmpty, End, EndLast, Ov, X1, X2) holds for K′ on the twin (Lemma C), with:
- the same side conditions;
- the same effect on (h, P, T);
- the same number of steps.
The domain D and the outside cases (o1)–(o7) are the same sets of parameters.
For reference, here is the abstract form both machines share. In it:
- Z: pairs with d = 0 and q ≥ 2;
touch (p,q,d) = (p+1,q-1,1-d);- ovp/ovpX: the parent's re-pairings.
Dec            (h; Z ++ (p,q+2,1) :: R; T)          -> (h+4; touch Z ++ (p+1,q+1,0) :: R; T)
DecMerge       (h; Z ++ (p,1,1) :: (p',q',d') :: R; T) -> (h+4; touch Z ++ (p+p'+3,q',d') :: R; T)
DecMergeTail   (h; Z ++ [(p,1,1)]; T1(t))           -> (h+4; touch Z; T1(p+t+3))
DecMergeEmpty  (h; Z ++ [(p,1,1)]; -)               -> (h+4; touch Z; T1(p+2))
End            (h; Z ++ [(p,q+2,0)]; -), V=0        -> (h+4; touch Z ++ [(p+1,q+1,0)]; T1(1))
EndLast        (h; Z ++ [(p,1,0)]; -), V=0          -> (h+4; touch Z; T1(p+4))
Ov             (h; (p1,q1,0) :: Z; T1(t)), V=0, p1>=2 -> (2; (h+5,p1-1,0) :: ovp q1 Z t; -)
X1             (h; (p1,q1,0) :: Z ++ [(pa,1,0);(pb,1,0)]; -), V=0, p1>=2 -> (2; (h+5,p1-1,0) :: ovpX q1 Z pa; T2(pb+3))
X2             (h; Z ++ [(p,q+2,0)]; T2(k)), V=0    -> (h+4; touch Z ++ [(p+1,q+1,0); (3,k,1)]; -)
As a check that does not go through Lemma C, 405 random rule instances (45 per rule, all h mod 4, sizes 2–300) were run on the twin's own table from mirrored words. They reach the predicted K′ exactly (§5).
6FamilyCheck: related machines are killed together or have a reason to be left open.
4 machines, 4 killed, 0 not. Family links: status.json parent, same transition table with another start (tools/dashboard.py), targeting.md follow-on rows, ledger "= twin" notes. A machine string named in a .v header / proof.md / notes.md is listed but does not make a family.
| who | machine | status | relation to this kill |
|---|---|---|---|
| #3 kill 4 | 1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB--- | ✓Killed: never halts | parent link; = #24's table mirrored, run from state B; targeting: follow-on to #3; named in #24's .v header; named in #24's proof.md; named in #24's notes.md; named in #3's notes.md · review · compared side by side above · mechanism |
| #25 kill 7 | 1RB1RF_1LC0LE_1RD0LB_1RA0RC_1RE1LB_0RD--- | ✓Killed: never halts | = #24's table mirrored, run from state D; named in #24's proof.md; named in #24's notes.md · review |
| #24 kill 8 | 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC--- | ✓Killed: never halts | this kill |
| #3b kill 12 | 1RB0RD_1RC1RF_1LD0LE_1RA0LC_1RE1LC_0RA--- | ✓Killed: never halts | = #24's table mirrored, run from state C; named in #3b's proof.md · review · mechanism |
7ChecklistCheck: every ✓ is computed; the two ○ are yours to decide; an amber ! is an optional check that did not finish.
- ✓Machine string exactthe .v literal == holdout list line 622 byte for byte
- ✓Statement is
~halts tm c0parsed from the .v and confirmed by check_kill (theorem_text, theorem_rocq) - ✓No axioms beyond baseline0 assumption(s); tools/assumptions_baseline.txt allows only functional_extensionality_dep
- ✓coqchk finished (optional)coqchk pass in 12.26 s
- ✓.v hash matches the checked hash.v = checked sha256 d3ce657f1502…; submission/ copy = checked sha256 d3ce657f1502…
- ✓No repo-local paths in the .vcomments name no path of ours (vendor/, machines/, tools/, rocq/, scripts/, reports/, atlas/, data/, journal/, /home/); busycoq's own
verify/X.vis fine: none in the .v or the submission/ copy - ✓Public write-up is cleantools/writeup_lint.py on
submission/proof.md: 0 error(s) - ○proof.md reviewed by Dennis (Checkpoint B)no Checkpoint B note from Dennis found
- notes.md L59: - No Checkpoint B notes from Dennis were on file when this was packaged. If he adds any, fold them into proof.md and the submission copy first.
- proof.md L1: # 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---: informal proof (DELTA against kill #3; Checkpoint B)
- proof.md L123: - Dennis's Checkpoint B reading (non-blocking).
- ○Family posted together?3 other kill(s) in the family: #3, #25, #3b; the Discord draft names 2 of them
Generated by tools/killreview.py at 2026-10-16 13:29 PDT in 0.1 s from the files linked above; nothing in this review is hand-written except the box “How we proved it never halts” (above), which quotes how_proved.md. Re-run: python3 -B tools/killreview.py 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---
Files
machines/<tm>/: 11 entries · raw notes, status, scripts, images
| name | size | changed |
|---|---|---|
| notes.md ↓ | 7.3 KB | 2026-10-10 10:24 |
| proof.md ↓ | 15 KB | 2026-10-10 10:12 |
| how_proved.md ↓ | 1.4 KB | 2026-10-14 10:51 |
| status.json ↓ | 650 B | 2026-10-13 06:44 |
| 1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---.v ↓ | 65 KB | 2026-10-10 17:25 |
| img/ | 5 items | 2026-10-16 10:29 |
| logs/ | 1 item | 2026-10-10 09:42 |
| rocq/ | 9 items | 2026-10-10 10:22 |
| submission/ | 6 items | 2026-10-12 12:46 |
| work/ | 2 items | 2026-10-12 12:41 |
| check_proof.py ↓ | 22 KB | 2026-10-10 09:57 |
status.json in full
{
 "tm": "1RB0RE_1LC0RA_1LD0LB_1LA1LF_1LE1RA_0LC---",
 "status": "KILLED_NONHALT",
 "stage": "done",
 "updated": "2026-10-10",
 "reason": "check_kill PASS, independently re-verified",
 "parent": "1RB0LD_1RC0RA_1RD1RF_1LA0LE_1RE1LD_0RB---",
 "relation": "twin of #3: #3's table mirrored and renamed, different start state, nearly identical run",
 "pr": "https://github.com/ccz181078/busycoq/pull/15",
 "pr_file": "verify/Skelet1LikeC2_1RB0RE.v",
 "pr_state": "merged",
 "pr_opened": "2026-10-10",
 "posted": "2026-10-10 (bbchallenge Discord #bb6, by Dennis)",
 "pr_comments": 0,
 "pr_merged_at": "2026-10-13T12:25:47Z",
 "pr_merged_by": "ccz181078"
}